
KillBot offers two integration methods: JavaScript (JS) and DNS. Both methods have their advantages but are designed for different tasks. Let's examine the difference, when DNS integration should be used, and why it's more effective in protecting against bots and attacks.
When to Use KillBot DNS Integration
DNS integration is necessary if you want to completely block bot access to your site — even before they can load any content. This is especially important if you:
- Protect contact data: For example, to prevent phone numbers from being stolen from your site. A common scheme now: competitors parse phone numbers, then get call details through mobile operators and call back these contacts. This is direct lead theft — potential clients you could have converted into sales.
-
Block price scraping: Prices are regularly scanned by competitors for price wars. DNS integration prevents bots from even starting to load the page.
-
Guard unique content: Articles, catalogs, product descriptions — all of this can be stolen and placed on competitor sites. DNS integration allows you to protect content originality and uniqueness.
-
Prevent HTTP DDoS attacks: This is one of the most common ways to crash a site. KillBot DNS integration acts as an external protective screen, filtering malicious traffic before it reaches the server.
When JS Integration is Sufficient
If your main task is analytics, ad traffic filtering, and flexible bot interaction, then JS integration is suitable.
KillBot JS integration allows you to:
- Determine if a visit is from a bot;
-
Display CAPTCHA to suspicious visits;
-
Collect analytics: who saw CAPTCHA, who passed it;
-
Create audiences for retargeting;
-
Filter non-target traffic in Yandex.Direct and other advertising systems.
However, it's important to understand: JS integration doesn't block access to content. Scripts load after the page is delivered to the browser, meaning bots can access data before being identified.
This limitation is related to the technology's nature: JavaScript executes in the client's browser, after HTML loads. Therefore, JS integration is better suited for analytics, data collection, and working with bots post-factum.
How to Configure KillBot DNS Integration
Configuring KillBot DNS integration doesn't require complex technical knowledge, but it's important to follow instructions precisely for KillBot's screen to effectively protect your site.
Step 1. Choosing Integration Type
In the KillBot dashboard:
- Set Up KillBot: https://my.kill-bot.net/script/get-code.
-
In the integration method section, select [DNS] Verification Page:
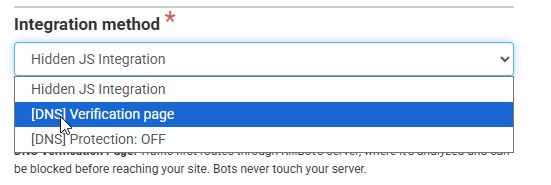
- Click the "Next" button.
After this, a page with DNS integration settings will open.
Step 2. Specifying Your Site's Server IP Address
The first and most important field — your server's IP address, i.e., the address your site should lead to after passing KillBot verification:
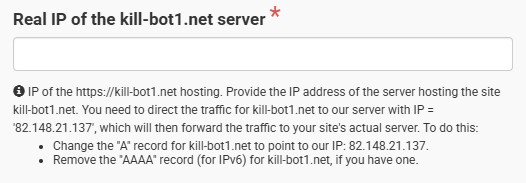
If you don't know the IP address — no problem. KillBot will determine and show the presumed IP. This value will be correct if your site isn't behind an external protective service like CloudFlare, StormWall, etc. In such cases, KillBot might determine the IP of an intermediate filter, not your server.
Verify that the specified IP actually belongs to your hosting.
Step 3. Selecting KillBot Server
Next, you need to choose which KillBot server will proxy traffic. This is necessary for geographical optimization and performance:
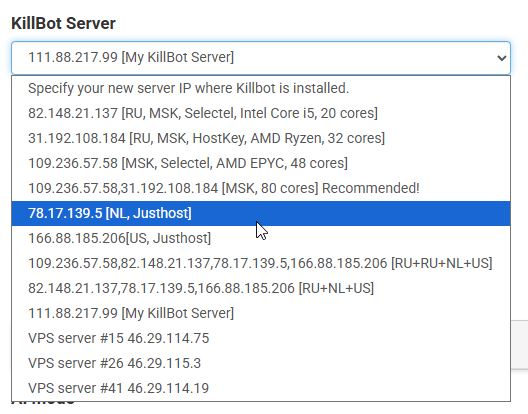
- If your site targets Russia — choose the Russian server in
Selectel. -
If the audience is from Europe or other regions — choose our Netherlands proxy server.
-
If you want to deploy KillBot on your own server, read: how to deploy KillBot on your own server
IMPORTANT: at this stage, your domain's DNS A-records (both with www and without www) must point to KillBot server's IP address — the one you selected from the list.
Also:
-
Mandatory: remove all AAAA records (for domain with
wwwand withoutwww) — these are IPv6 records that KillBot currently doesn't support. - Ensure only one A-record exists. If additional A-records remain in DNS, site hanging errors may occur.
- There should be only one A-record pointing to KillBot server.
How DNS Integration Works
After completing setup:
- All requests to your site will first go to KillBot's proxy server.
-
There, each visit undergoes verification.
-
Bots can be blocked, looped, or receive CAPTCHA (this is configurable, by default CAPTCHA is only shown to bots).
-
Legitimate visitors are instantly redirected to your server without delays.
Step 4. Configuration for Sites Behind Proxy Protection (CloudFlare, StormWall, etc.)
In this case use "a self-signed certificate":
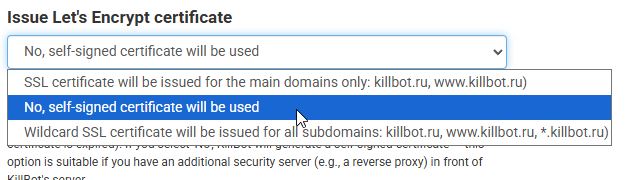
What Does This Setting Do?
If your site is already protected by an external service (e.g., CloudFlare), it's hidden behind another proxy server, making standard Let's Encrypt SSL certificate issuance impossible. In this case, KillBot:
- Disables Let's Encrypt certificate issuance.
-
Issues a self-signed certificate that doesn't require domain verification.
-
Doesn't verify that your DNS already points to KillBot — everything activates immediately.
Why is This Important?
If KillBot is first in the chain (i.e., it's at the front and directly interacts with visitors), then a full SSL certificate from Let's Encrypt or another trusted authority is necessary.
If KillBot is behind another proxy (e.g., behind CloudFlare), browsers don't see it directly — and a self-signed certificate is sufficient. This is standard practice in infrastructure with multiple proxy levels.
CloudFlare Configuration Specifics
For everything to work correctly:
-
Go to CloudFlare (or other proxy) settings:
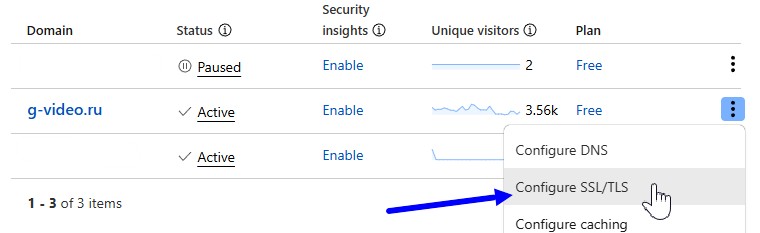
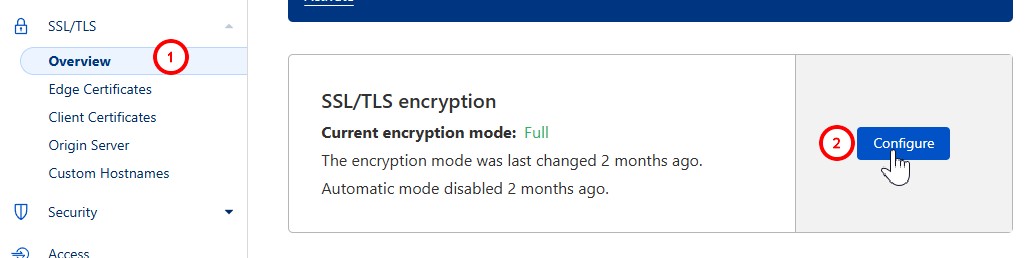
-
In the SSL section, select "Full" mode.
- This tells CloudFlare not to verify whether KillBot's certificate is trusted:
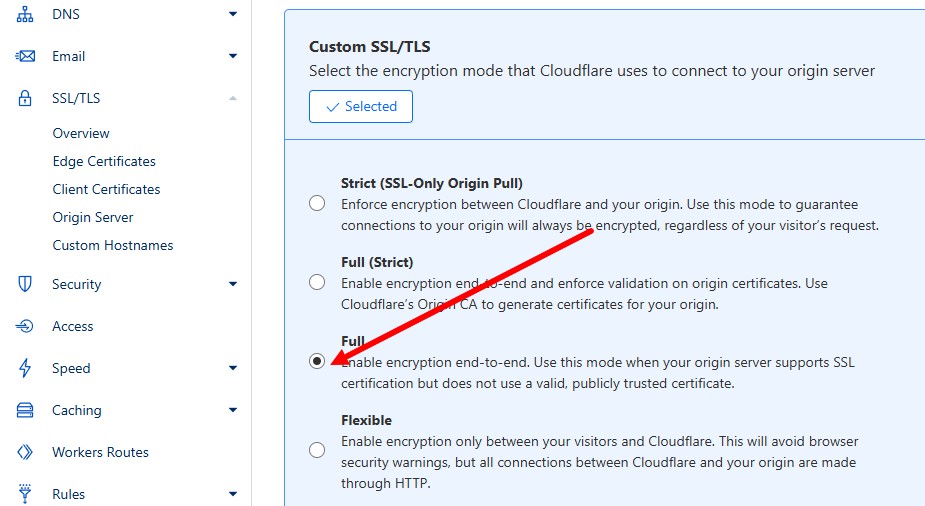
-
Otherwise (if "Strict" mode is selected), CloudFlare might block the connection due to the self-signed certificate.
💡 Such a scheme is standard practice when integrating with CDN, protective proxies, and other intermediaries. Self-signed certificates are used between services that don't require public certificate trust.
Step 5. Exception Configuration: IP Addresses and User-Agents
After selecting the DNS proxy server, you need to configure exceptions to avoid blocking important technical connections, like payment system callbacks or analytics service requests.
IP Addresses with Access Without Verification
By default, KillBot DNS proxy blocks all HTTP requests without JavaScript support, except verified search bots.
Important: search engines, including Google, Yandex, and others, will continue indexing the site without problems. KillBot can clearly distinguish real search robots from fake ones and won't cause the site to drop from search results.
To allow site access without verification:
-
Enter IP addresses of services that need access:
- Payment systems (e.g., callbacks from YooKassa, Tinkoff, CloudPayments, etc.).
-
External APIs or analytics, like Amplitude, Segment, etc.
-
IP format:
-
Specify IP address beginning, and all addresses starting with these digits will be allowed.
-
Example:
-
123.123— will allow all IPs from123.123.0.0to123.123.255.255. -
10.10.10.10— will allow only one specific IP.
-
-
Allowed User-Agents
If you don't have an exact IP but know the service's User-Agent (e.g., search bot or technical scanner), you can allow it by User-Agent.
Allowed User-Agent must contain all words separated by dots.
Examples:
-
If you want to allow Yandex bot:
-
Enter
yandex.botand KillBot will allow User-Agent containing both "yandex" and "bot".
-
-
If you need to allow Bing:
-
Specify
bing.bot.
-
This way, KillBot will verify that both words are contained in the string and only then allow access.